Telegram & WhatsApp Web Login: Security, Privacy & Setup Guide
Learn how to use Telegram and WhatsApp Web securely. Explore official login methods, QR authentication, session management, privacy settings, and enterprise security practices.
The convenience of accessing messaging platforms through desktop browsers and native applications has fundamentally transformed how individuals and organizations communicate, collaborate, and conduct business. Telegram Web and WhatsApp Web extend mobile-first messaging ecosystems onto desktop environments enabling keyboard-efficient typing, file transfer at scale, multi-window workflows, and seamless integration with browser-based productivity tools. Yet this convenience introduces attack surfaces absent from mobile-only usage: browser session hijacking, QR code interception, persistent session exploitation on shared devices, malicious browser extensions capturing authentication tokens, and supply chain attacks through counterfeit download sources. Understanding the complete technical lifecycle—from secure acquisition through authenticated session establishment to ongoing session hygiene and eventual termination—isn't optional security awareness; it's operational prerequisite for anyone using these platforms in professional, sensitive, or high-risk contexts.
This guide provides comprehensive technical coverage of downloading and authenticating Telegram Web and WhatsApp Web securely. We'll examine platform-specific download verification methodologies preventing malware-infected counterfeit clients, decode authentication protocols and cryptographic handshakes establishing secure sessions, analyze session persistence mechanisms and their security implications, compare privacy architectures determining what data each platform exposes during web usage, establish multi-device synchronization best practices balancing convenience with security, address enterprise deployment considerations for organizational use, and provide incident response protocols for compromised sessions. Whether you're an individual user seeking secure desktop messaging access, an IT administrator deploying messaging platforms across an organization, a security professional assessing communication tool risk profiles, or a privacy-conscious user evaluating platform trade-offs, this guide delivers the technical depth needed to use Telegram Web and WhatsApp Web confidently and securely.
Let's begin by understanding why download source verification matters more than most users realize—and how counterfeit clients have become sophisticated attack vectors.
Chapter 1: Secure Download and Installation — Verifying Authenticity Before First Launch
The attack surface begins before authentication. Malicious actors distribute counterfeit Telegram and WhatsApp clients through search engine ads, third-party app stores, forum posts, and phishing emails. These counterfeits may function identically to legitimate clients while silently exfiltrating messages, contacts, media, and authentication credentials. Verification isn't paranoia; it's foundational security practice.
Telegram Download Verification
Official Source Identification: Telegram maintains a single authoritative download directory at Telegram Official Download Page (dofollow) listing verified applications for Windows, macOS, Linux, Android, iOS, and web browsers. This page links directly to official distribution channels: Microsoft Store, Mac App Store, GitHub releases for desktop clients, and direct APK downloads for Android. Any download source not reachable through this official directory should be treated as potentially compromised. Bookmark this page; never rely on search engine results which frequently surface sponsored counterfeit listings above official results.
Open-Source Verification Advantage: Telegram desktop clients are open-source with code publicly available on GitHub. This transparency enables independent security auditing and binary verification. Advanced users can compile clients from source ensuring code-binary correspondence. For non-developers, verify downloaded binaries against published checksums (SHA-256 hashes) listed on official release pages. Checksum mismatch indicates tampering or corruption; never execute mismatched binaries. GPG signature verification provides additional authenticity confirmation using Telegram's published signing keys. Open-source availability doesn't guarantee security but enables verification impossible with closed-source alternatives.
Browser Extension Caution: Multiple third-party browser extensions claim to enhance Telegram Web functionality. Most are unnecessary; official Telegram Web operates natively without extensions. Third-party extensions request broad permissions enabling message reading, contact access, and keystroke logging. Install only extensions from verified developers with transparent privacy policies and auditable source code. Prefer official Telegram integrations over community alternatives. Extension permissions should be reviewed periodically; excessive permissions indicate potential data harvesting.
Web Client Access Protocol: Telegram Web accessible at web.telegram.org requires no installation reducing supply chain attack surface. Verify URL exactly; typosquatting domains (web-telegram.org, telegram-web.com, etc.) are common phishing vectors. Check TLS certificate validity confirming legitimate Telegram Inc. ownership. Use bookmark rather than manual URL entry preventing typo exploitation. Web client receives automatic security updates without user action; desktop clients require manual update verification.
WhatsApp Download Verification
Official Distribution Channels Only: WhatsApp distributes exclusively through official app stores (Microsoft Store, Mac App Store) and whatsapp.com/download. No legitimate WhatsApp desktop client exists outside these channels. Third-party "WhatsApp Plus," "GBWhatsApp," or modified clients violate terms of service, lack security updates, and frequently contain malware. WhatsApp Web accessed at web.whatsapp.com requires no installation; verify URL and TLS certificate before authentication. WhatsApp doesn't offer browser extensions; any extension claiming WhatsApp integration is unofficial and potentially malicious.
Desktop Client vs. Web Client Decision: WhatsApp Desktop (native application) and WhatsApp Web (browser-based) share identical functionality but differ in security characteristics. Desktop clients receive automatic updates through app store mechanisms reducing update lag. Web clients eliminate installation attack surface but inherit browser vulnerabilities and extension risks. Desktop clients maintain separate process isolation from browser environment reducing cross-contamination risk. Web clients enable usage on restricted devices where software installation prohibited. Choose based on threat model: desktop preferred for primary workstations; web acceptable for temporary/shared device access with enhanced session hygiene.
Update Verification Discipline: WhatsApp desktop updates distributed through app stores include cryptographic signatures verifying publisher authenticity. Manual updates downloaded from whatsapp.com should be verified against published checksums. Enable automatic updates reducing exposure window between vulnerability disclosure and patch application. Delayed updates represent significant risk; WhatsApp frequently patches critical vulnerabilities. Monitor WhatsApp security advisories for urgent updates requiring immediate action.
Platform Comparison: Download Security Posture
|
Factor
|
Telegram
|
WhatsApp
|
|---|---|---|
|
Open Source
|
Yes (desktop/web)
|
No
|
|
Binary Verification
|
Checksums + GPG signatures
|
App store signatures only
|
|
Web Client Availability
|
Yes (official)
|
Yes (official)
|
|
Third-Party Clients
|
Exist (unofficial, risky)
|
Exist (unofficial, risky)
|
|
Browser Extensions
|
Community-created (risky)
|
None official
|
|
Update Mechanism
|
Manual/auto depending on platform
|
App store auto-update
|
|
Source Code Auditability
|
High
|
None
|
Telegram's open-source nature provides verification advantages unavailable to WhatsApp users. WhatsApp's closed ecosystem simplifies trust model to app store verification but prevents independent audit. Both platforms require disciplined source verification; neither is immune to counterfeit distribution.
Chapter 2: Authentication Protocols and Session Establishment
Understanding authentication mechanics reveals security properties and vulnerability points in the login process.
QR Code Authentication Mechanics
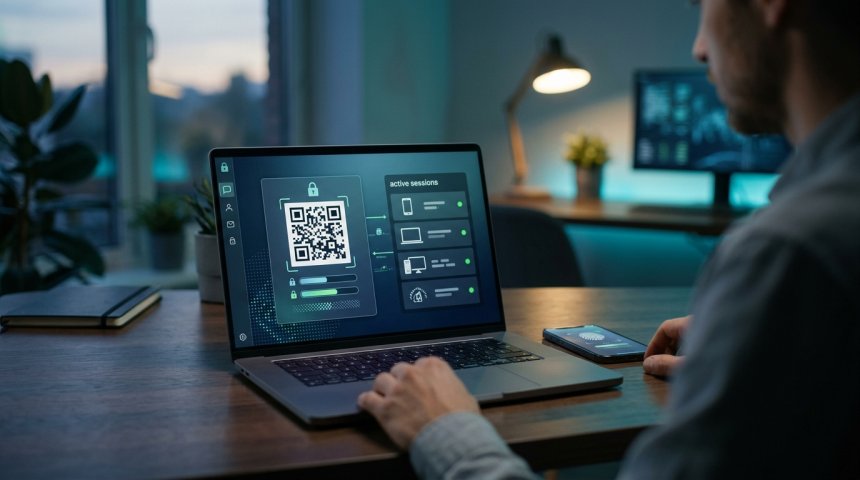
How QR Login Works: Both platforms use QR code scanning as primary desktop authentication method. Desktop client/web page generates ephemeral QR code encoding session token and public key. Mobile app scans QR, decrypts token, verifies against server, and authorizes desktop session. Cryptographic handshake establishes encrypted channel between mobile and desktop without transmitting plaintext credentials. QR codes expire after 30-60 seconds preventing replay attacks.
Security Properties: QR authentication avoids password transmission eliminating credential theft vectors. Ephemeral tokens prevent reuse. Mobile device acts as authentication factor requiring physical possession. Encrypted channel protects session establishment from network eavesdropping. Server-mediated verification prevents man-in-the-middle attacks assuming server trustworthiness.
Vulnerability Points: QR codes visible on screen can be photographed remotely enabling unauthorized session establishment if attacker possesses victim's unlocked mobile device. Screen sharing during QR display exposes authentication to meeting participants. Malicious browser extensions can capture QR codes before display. Compromised mobile device enables unrestricted desktop session authorization. Physical access to unlocked desktop during QR display window enables opportunistic scanning.
Mitigation Strategies: Never display QR codes during screen sharing or in publicly visible locations. Verify mobile device security before scanning (lock screen enabled, biometric protection active, no malware indicators). Scan QR codes promptly minimizing exposure window. Log out immediately after accidental exposure. Monitor active sessions regularly detecting unauthorized access. Use platform-specific session verification features confirming authorized device list.
Phone Number Authentication (Telegram Alternative)
SMS/Call Verification Option: Telegram offers phone number authentication as QR alternative for desktop clients. User enters phone number, receives SMS/call verification code, enters code on desktop. This method bypasses mobile app dependency enabling authentication when mobile device unavailable.
Security Trade-offs: Phone authentication vulnerable to SIM swapping, SS7 protocol exploits, and SMS interception. Verification codes transmitted over insecure channels potentially interceptable. Doesn't require mobile app possession reducing authentication factor strength. Convenient for recovery scenarios but weaker security posture than QR authentication. Prefer QR authentication when mobile app accessible; reserve phone authentication for recovery or mobile-unavailable situations.
Code Handling Best Practices: Never share verification codes with anyone including purported support representatives. Enter codes only in official client interfaces. Codes expire quickly; request new codes rather than reusing expired ones. Monitor for unexpected verification requests indicating account compromise attempts. Enable two-step verification adding password layer beyond SMS/call verification significantly strengthening phone authentication security.
Session Token Architecture
Token Generation and Storage: Successful authentication generates session token stored locally on desktop device. Tokens enable persistent login without repeated authentication. Token storage location varies: browser localStorage/sessionStorage for web clients, encrypted keychain/credential store for desktop clients. Token expiration policies differ: Telegram sessions persist indefinitely until manual logout; WhatsApp sessions expire after extended inactivity or explicit logout.
Token Security Implications: Persistent tokens create long-lived attack surfaces. Device compromise exposes all active sessions. Shared device usage without logout grants subsequent users account access. Browser profile syncing propagates tokens across devices potentially extending compromise scope. Token theft enables session hijacking without credential knowledge. Regular session auditing and proactive logout on untrusted devices essential.
Token Revocation Mechanisms: Both platforms enable remote session termination from mobile app. Telegram: Settings → Devices → terminate individual or all sessions. WhatsApp: Settings → Linked Devices → log out individual or all devices. Remote revocation critical for lost/stolen devices, suspected compromise, or post-session hygiene on shared devices. Revocation takes effect immediately invalidating stolen tokens. Regular revocation of unused sessions reduces attack surface.
For detailed technical documentation on WhatsApp's authentication protocols, encryption implementation, and session security architecture, the WhatsApp Security White Paper (nofollow) provides comprehensive specification enabling informed security assessment and compliance evaluation.
Chapter 3: Privacy Architecture Comparison — What Each Platform Exposes During Web Usage
Privacy isn't binary; it's architectural. Telegram and WhatsApp implement fundamentally different privacy models affecting what data web sessions expose to servers, network observers, and client-side threats.
Encryption Model Differences
WhatsApp: End-to-End Encryption Default All WhatsApp messages, calls, and media encrypted end-to-end using Signal Protocol. Web sessions participate in E2EE through cryptographic linkage with mobile device. Server cannot decrypt message content even during web relay. Metadata (sender, recipient, timestamp, message size) visible to server. E2EE applies uniformly across mobile and web; no configuration required. Backup encryption optional but recommended preventing cloud backup exposure.
Telegram: Hybrid Encryption Model Telegram default chats use client-server encryption (MTProto 2.0) where server holds decryption keys enabling multi-device sync and cloud storage. Secret Chats use E2EE but aren't available on web/desktop clients—mobile only. Web sessions access server-encrypted chats meaning Telegram servers can technically access message content. This architecture enables features WhatsApp cannot offer (cloud sync, multi-device independence, message editing) but sacrifices E2EE universality. Users must consciously choose Secret Chats for E2EE and accept web inaccessibility trade-off.
Privacy Implications: WhatsApp web sessions maintain E2EE confidentiality assuming mobile device security. Telegram web sessions trust Telegram servers with message content by design. Threat models differ: WhatsApp protects against server compromise; Telegram protects against network eavesdropping but not server access. Choose based on adversary model: state-level adversaries capable of server compromise favor WhatsApp E2EE; casual eavesdroppers adequately mitigated by either platform's transport encryption.
Metadata Exposure Profiles
WhatsApp Metadata: Server observes: sender/receiver phone numbers, message timestamps, message sizes, group membership, online status, last seen timestamps, profile photo updates, status updates. Metadata retained for service operation duration. Law enforcement requests can compel metadata disclosure. Metadata sufficient for social graph reconstruction and behavioral analysis despite content encryption.
Telegram Metadata: Server observes: user IDs, contact lists (if synced), message timestamps, chat participation, online status, IP addresses, device information. Cloud-stored messages accessible to server. Telegram retains less metadata than WhatsApp by policy but technical capability exists due to server-side decryption. Secret Chat metadata minimal but web-inaccessible.
Metadata Minimization Strategies: Both platforms: disable contact syncing, limit profile information, use username instead of phone number (Telegram), disable read receipts and online status visibility. WhatsApp-specific: minimize group participation exposing phone numbers to all members. Telegram-specific: use Secret Chats for sensitive communications accepting web inaccessibility. Metadata reduction complements but doesn't replace encryption; assume metadata observable regardless of settings.
Client-Side Data Storage
Browser Storage (Web Clients): Web clients store session tokens, cached messages, and media in browser storage mechanisms. Clearing browser data terminates sessions and removes cached content. Private/incognito mode prevents persistent storage but sacrifices convenience. Browser extensions can access storage contents creating data exposure risk. Browser compromise exposes all stored messaging data.
Desktop Client Storage: Native clients store data in application directories with OS-level protection. Encryption at rest varies: WhatsApp Desktop encrypts local database; Telegram Desktop stores unencrypted by default (configurable). Disk encryption (FileVault, BitLocker) provides additional protection layer. Forensic tools can extract data from unencrypted stores. Secure deletion practices important for sensitive communications on shared or decommissioned devices.
Data Retention Hygiene: Regularly clear cached media and message history on web/desktop clients reducing exposure from device compromise. Configure auto-delete timers for sensitive conversations (Telegram feature; WhatsApp limited). Avoid storing sensitive media locally; use ephemeral viewing when available. Logout and clear data after shared device usage. Data minimization reduces breach impact when prevention fails.
Chapter 4: Multi-Device Synchronization and Session Management
Modern messaging platforms support multiple concurrent sessions creating convenience and complexity simultaneously.
Telegram Multi-Device Architecture
Independent Session Model: Telegram treats each device as independent session with full message history synchronized through cloud. New devices receive complete chat history upon authentication (except Secret Chats). Sessions operate independently; actions on one device don't require others being online. Unlimited concurrent sessions supported. This architecture enables seamless multi-device workflows but expands attack surface proportionally.
Session Visibility and Control: Settings → Devices displays all active sessions with device type, location, IP address, and last active timestamp. Individual or bulk session termination available. Session notifications alert when new devices authenticate enabling rapid unauthorized access detection. Granular session control supports security-conscious users managing complex device ecosystems.
Cloud Sync Security Trade-offs: Cloud synchronization enables convenient multi-device access but means Telegram servers store decryptable message history. Compromised account exposes entire message history across all time. Two-step verification adds password requirement for new device authentication preventing account takeover from SMS interception alone. Recovery email/code setup essential preventing permanent account loss from forgotten passwords. Balance convenience against exposure; consider whether cloud sync justifies E2EE sacrifice for your threat model.
WhatsApp Multi-Device Architecture
Linked Device Model: WhatsApp's multi-device beta (now standard) links up to four companion devices plus primary phone. Companion devices receive message history for limited lookback period (typically 30 days). Primary phone remains authoritative; certain features require phone connectivity. Companion devices operate independently once linked but periodic phone check-in maintains linkage. More restrictive than Telegram but maintains stronger E2EE guarantees.
Linked Device Management: Settings → Linked Devices shows all connected devices with browser/platform identification and last active timestamp. Individual or bulk logout available. QR code linking requires phone unlock ensuring physical possession during authorization. New device notifications sent to primary phone enabling unauthorized linking detection. Device limit prevents unlimited session proliferation reducing attack surface versus Telegram.
Synchronization Limitations: Companion devices may experience delayed message delivery during phone offline periods. Certain message types (location sharing, live location, some media) require phone connectivity. Broadcast lists and some group features limited on companion devices. Limitations reflect E2EE architecture constraints; accepting limitations preserves security properties. Evaluate whether limitations impact your workflow; if so, assess whether convenience gain justifies security trade-off.
Session Hygiene Best Practices
Regular Session Auditing: Review active sessions weekly minimum; daily for high-risk users. Terminate unrecognized or unused sessions immediately. Document expected device list enabling anomaly detection. Session auditing catches compromise indicators before significant damage occurs. Make auditing habitual not reactive.
Shared Device Protocols: Never remain logged in on shared/public devices. Use private/incognito browser mode preventing persistent session storage. Logout explicitly after each session; closing browser tab insufficient for persistent sessions. Clear browser cache and cookies after logout removing residual authentication artifacts. Assume shared devices compromised; avoid sensitive communications entirely when possible.
Travel and Border Crossing Considerations: Border agents in some jurisdictions demand device unlocking and account access. Pre-travel preparation: logout all web/desktop sessions, enable two-step verification, remove sensitive chat history, consider temporary travel devices without messaging access. Post-crossing: verify session integrity, check for unauthorized access, rotate credentials if compromise suspected. Legal obligations vary by jurisdiction; understand your rights and risks before travel.
Compromise Response Protocol: Suspected session compromise requires immediate action: (1) Terminate all sessions from trusted mobile device, (2) Change account password/PIN if applicable, (3) Enable/reconfigure two-step verification, (4) Review recent message activity for unauthorized actions, (5) Notify contacts of potential compromise if messages sent from compromised session, (6) Scan devices for malware before re-authentication, (7) Monitor account activity closely for 30 days post-incident. Rapid response limits damage; delayed response enables escalation.
Chapter 5: Enterprise Deployment and Organizational Security
Organizations using Telegram or WhatsApp Web face amplified risks requiring structured governance.
Policy Development Framework
Acceptable Use Policies: Define permitted use cases, prohibited content types, approved platforms, and mandatory security controls. Distinguish personal versus organizational use clarifying expectations and liability. Address BYOD scenarios specifying security requirements for personal devices accessing organizational communications. Policy should be specific enough to guide behavior without being so restrictive that employees circumvent controls. Regular policy review ensures alignment with evolving threats and platform capabilities.
Data Classification Integration: Map messaging platform usage to data classification scheme. Prohibit classified/sensitive data transmission over platforms lacking appropriate encryption (e.g., Telegram non-Secret Chats for confidential data). Define retention requirements aligned with regulatory obligations. Specify approved alternatives for sensitive communications (Signal, Wire, enterprise platforms with administrative controls). Classification-aware usage prevents inadvertent sensitive data exposure through inappropriate platform selection.
Incident Response Integration: Incorporate messaging platform compromise into organizational incident response plan. Define reporting procedures, containment steps, notification obligations, and forensic preservation requirements. Train staff on recognizing and reporting compromise indicators. Test response procedures through tabletop exercises validating effectiveness. Messaging incidents often escalate quickly due to real-time communication nature; prepared response prevents chaos.
Technical Controls and Monitoring
Network-Level Controls: Implement DNS filtering blocking known malicious messaging-related domains. Proxy inspection for web client traffic identifying anomalous patterns (though E2EE limits content inspection). Firewall rules restricting messaging platform access to authorized networks/devices. Network segmentation isolating messaging traffic from critical systems. Network controls complement but don't replace endpoint security; layered defense essential.
Endpoint Protection Integration: Deploy EDR/XDR solutions monitoring messaging client behavior for anomalies. Application whitelisting preventing unauthorized client installations. Browser extension management controlling approved extensions. Device encryption protecting stored messaging data. Patch management ensuring clients and browsers current. Endpoint controls address client-side threats network controls cannot see.
Identity and Access Management: Integrate messaging platforms with SSO where supported enabling centralized authentication and deprovisioning. Conditional access policies restricting access based on device compliance, location, and risk score. Automated deprovisioning upon employee departure preventing orphaned sessions. MFA enforcement for all messaging platform access. IAM integration brings messaging access under organizational identity governance reducing shadow IT risk.
Compliance and Legal Considerations
Regulatory Alignment: Assess messaging platform usage against applicable regulations: GDPR (EU data protection), HIPAA (healthcare), FINRA (financial services), attorney-client privilege (legal), export controls (international communications). Many regulations impose specific requirements messaging platforms may not satisfy natively. Document compliance gaps and mitigation strategies. Legal review before organizational adoption prevents regulatory violations.
E-Discovery and Retention: Messaging content may be subject to litigation holds, regulatory requests, or internal investigations. Platform-native retention controls may be insufficient for legal hold requirements. Implement supplemental archiving solutions capturing messaging content for compliant retention. Ensure archiving respects encryption and privacy commitments. E-discovery capability should be established before need arises; reactive implementation during litigation problematic.
Cross-Border Data Transfer: Messaging platforms transmit data across borders potentially triggering data transfer restrictions. Assess data flows against applicable transfer mechanisms (Standard Contractual Clauses, adequacy decisions, binding corporate rules). Document transfer basis for compliance demonstration. Cross-border transfer issues particularly relevant for multinational organizations using platforms with unclear data residency practices.
Chapter 6: Threat Landscape and Defensive Measures
Understanding active threats enables proactive defense rather than reactive remediation.
Common Attack Vectors
QR Code Interception: Attackers photograph QR codes from screens during meetings, video calls, or public displays. Captured QR scanned with attacker's device establishing unauthorized session if victim's phone accessible or compromised. Defense: never display QR codes in observable contexts, use phone authentication when QR exposure unavoidable, monitor active sessions for unauthorized devices, terminate suspicious sessions immediately.
Session Hijacking via Browser Compromise: Malicious browser extensions, XSS vulnerabilities, or compromised browsers steal session tokens from storage. Stolen tokens enable attacker access without authentication. Defense: minimize browser extensions, keep browsers updated, use dedicated browser profiles for messaging, enable browser sandboxing, monitor for unauthorized session activity, logout after sensitive sessions on shared browsers.
Phishing and Social Engineering: Attackers impersonate platform support requesting verification codes, session tokens, or account credentials. Fake login pages capture authentication inputs. Defense: never share verification codes, verify URLs before authentication, enable two-step verification preventing code-only compromise, educate users on social engineering tactics, report phishing attempts to platforms.
Malware and Keyloggers: Endpoint malware captures keystrokes, screenshots, or clipboard contents exposing messages and credentials. Defense: endpoint protection with behavioral detection, application whitelisting, regular malware scanning, device encryption, secure boot, principle of least privilege reducing malware impact. Assume compromised devices expose all messaging; isolate and remediate before continued use.
Supply Chain Attacks: Compromised download sources distribute malware-infected clients. Update mechanisms hijacked delivering malicious payloads. Defense: download only from official sources, verify checksums/signatures, enable automatic updates from trusted channels, monitor security advisories for supply chain incidents, maintain offline installer copies for emergency recovery.
Advanced Defensive Measures
Dedicated Messaging Devices: High-risk users benefit from dedicated devices used exclusively for sensitive communications. Dedicated devices reduce cross-contamination risk from general-purpose computing activities. Device hardened with minimal applications, strict update discipline, and physical security controls. Cost and inconvenience justified for journalists, activists, executives handling sensitive information, and personnel in adversarial environments.
Network Isolation: Messaging traffic routed through isolated network segment or VPN preventing lateral movement from compromised messaging sessions. Guest networks for personal messaging on organizational infrastructure. Network isolation contains breach impact limiting attacker pivot opportunities. Implementation complexity balanced against risk profile.
Behavioral Monitoring: Anomaly detection identifying unusual messaging patterns: off-hours activity, geographic anomalies, volume spikes, recipient changes, attachment frequency increases. Behavioral baselines established during normal operation enabling deviation detection. Alerts trigger investigation before damage escalates. Privacy-respecting implementation focuses on metadata patterns not content inspection.
Security Awareness Training: Regular training covering messaging-specific threats, safe authentication practices, session hygiene, social engineering recognition, and incident reporting. Training tailored to organizational context and threat landscape. Practical exercises reinforcing concepts beyond theoretical knowledge. Training effectiveness measured through simulated phishing tests and behavioral metrics. Human factor remains strongest defense when technical controls fail.
Chapter 7: Platform Selection Framework — Choosing Based on Technical Requirements
Platform choice should reflect technical requirements not marketing claims or social pressure.
Decision Matrix
|
Requirement
|
Telegram
|
WhatsApp
|
Winner
|
|---|---|---|---|
|
E2EE for all messages
|
No (Secret Chats only, no web)
|
Yes (default)
|
WhatsApp
|
|
Multi-device independence
|
Yes (full cloud sync)
|
Limited (phone-dependent)
|
Telegram
|
|
Large file transfer
|
Up to 2GB
|
Up to 2GB
|
Tie
|
|
Group size limit
|
200,000 members
|
1,024 members
|
Telegram
|
|
Bot/API integration
|
Extensive
|
Limited Business API
|
Telegram
|
|
Open-source verification
|
Yes
|
No
|
Telegram
|
|
Metadata minimization
|
Moderate
|
Higher exposure
|
Telegram
|
|
Regulatory acceptance
|
Variable
|
Wider enterprise acceptance
|
WhatsApp
|
|
Self-destructing messages
|
Yes (Secret Chats)
|
Limited (view once)
|
Telegram
|
|
Username-based contact
|
Yes
|
Phone number required
|
Telegram
|
Threat Model Alignment
State-Level Adversary: Prioritize E2EE (WhatsApp) or Telegram Secret Chats with mobile-only access. Assume server compromise. Minimize metadata exposure. Use dedicated devices. Consider Signal for highest assurance.
Corporate Espionage: WhatsApp E2EE protects content; Telegram cloud sync enables convenient collaboration with accepted server trust. Implement organizational controls regardless of platform. Classify data appropriately.
Casual Privacy: Either platform adequate with proper configuration. Focus on session hygiene, metadata minimization, and update discipline. Convenience may justify Telegram's cloud features.
Organizational Deployment: WhatsApp Business API enables controlled deployment with compliance integration. Telegram bots enable automation but require security review. Evaluate against regulatory requirements and IT governance capabilities.
High-Risk Journalism/Activism: Signal preferred over both platforms. If Telegram/WhatsApp required, use Secret Chats (Telegram mobile only) or WhatsApp E2EE with hardened devices. Assume surveillance. Operational security training essential.
Migration Considerations
Switching platforms requires data migration planning, contact notification, and transition period management. Export/import capabilities vary: Telegram supports chat export; WhatsApp limited export options. Contact migration manual for both platforms. Transition period maintains both platforms running ensuring communication continuity. Communicate migration timeline to contacts preventing missed messages. Post-migration verification confirms complete transition before decommissioning old platform.
Conclusion: Convenience Without Complacency
Telegram Web and WhatsApp Web deliver genuine productivity benefits extending messaging into desktop workflows. These benefits come with expanded attack surfaces requiring deliberate security practices. Secure download verification, understanding authentication protocols, maintaining session hygiene, respecting privacy architecture differences, implementing organizational controls, and staying informed about evolving threats aren't burdensome overhead—they're the price of admission for secure desktop messaging.
Security isn't product feature; it's ongoing practice. Platforms evolve, threats adapt, and user behaviors drift. Regular reassessment ensures defenses match current realities. Complacency accumulated through months of incident-free usage creates vulnerability precisely when attention wanes. Maintain discipline. Verify habitually. Question assumptions. Update continuously.
Your communications carry value worth protecting. The platforms provide tools; you provide judgment. Use both wisely. The intersection of convenience and security isn't compromise—it's competence. Build it deliberately. Maintain it actively. Communicate confidently.
Frequently Asked Questions (FAQs)
Is it safe to use Telegram Web or WhatsApp Web on public/shared computers?
Technically possible but security-risky. If necessary: use private/incognito browser mode preventing persistent session storage, never save login credentials, logout explicitly after each session (closing tab insufficient), clear browser cache/cookies/storage after logout, avoid sensitive communications entirely, verify URL and TLS certificate before authentication, and assume the device may be compromised. Better alternative: use mobile app exclusively on personal device when accessing sensitive communications. Public computers should be treated as hostile environments suitable only for non-sensitive, disposable interactions. If regular shared-computer usage required, consider dedicated portable browser on USB drive with pre-configured security settings reducing reliance on host system integrity. Never enter verification codes on shared computers if phone visible to others; QR code interception risk elevated in public environments.
Can someone hack my account through Telegram Web or WhatsApp Web?
Direct hacking of encrypted sessions extremely difficult but session hijacking through indirect methods occurs regularly. Primary attack vectors: QR code interception during display, session token theft via malicious browser extensions or malware, phishing capturing verification codes, SIM swapping enabling phone authentication bypass, and physical access to unlocked devices. Prevention: enable two-step verification (critical), monitor active sessions regularly, never display QR codes in observable contexts, minimize browser extensions, keep software updated, use dedicated browser profiles, logout from shared devices, and maintain mobile device security. Two-step verification alone prevents majority of account takeover attempts by requiring password/PIN beyond SMS code. If compromise suspected: immediately terminate all sessions from trusted mobile device, change passwords, enable/reset two-step verification, scan devices for malware, and notify contacts of potential unauthorized messages.
What's the difference between Telegram Web and Telegram Desktop in terms of security?
Telegram Desktop (native application) offers superior security versus Telegram Web (browser-based) in several dimensions: process isolation from browser environment reducing cross-contamination risk, optional local database encryption protecting stored messages, automatic update mechanisms ensuring timely patches, reduced exposure to malicious browser extensions, and GPG-signed binaries enabling authenticity verification. Telegram Web advantages: no installation required reducing supply chain attack surface, automatic server-side updates, accessibility on restricted devices. Both share identical server-side security properties (MTProto 2.0 encryption, cloud storage). Recommendation: prefer Desktop for primary workstations; reserve Web for temporary/shared device access with enhanced session hygiene. Neither provides E2EE for standard chats; Secret Chats (E2EE) available only on mobile apps. Choose based on threat model balancing convenience against security requirements.
How do I know if my WhatsApp Web or Telegram Web session has been compromised?
Indicators include: unrecognized devices in active session list, messages you didn't send appearing in chat history, contacts reporting unexpected messages from your account, verification codes received without initiating login, unusual online status activity during your offline periods, new linked devices you didn't authorize, and settings changes you didn't make. Both platforms provide active session/device lists showing device type, location, IP address, and last active timestamp—review these regularly (weekly minimum, daily for high-risk users). Enable login notifications alerting you to new session establishments. If compromise detected: immediately terminate all sessions from trusted mobile device, enable/reset two-step verification, change associated passwords, scan all devices for malware, review recent message activity for unauthorized actions, notify contacts of potential compromise, and monitor account closely for 30 days. Document incident details supporting potential law enforcement reporting or platform support escalation.
Should organizations use Telegram or WhatsApp for business communications?
Depends on organizational requirements, regulatory environment, and threat model. WhatsApp advantages: universal E2EE, broader enterprise acceptance, Business API enabling controlled deployment, familiar user base reducing training burden. Telegram advantages: superior bot/API ecosystem enabling automation, larger group capacity, cloud sync enabling multi-device workflows, open-source verifiability, username-based contact avoiding phone number exposure. Critical considerations: Telegram standard chats NOT end-to-end encrypted making unsuitable for confidential business communications without Secret Chats (mobile-only); WhatsApp E2EE protects content but metadata exposure higher; neither platform provides enterprise administrative controls comparable to dedicated business messaging platforms (Slack, Teams, Wire); regulatory compliance (HIPAA, FINRA, GDPR) may prohibit either platform for regulated data. Recommendation: conduct formal risk assessment evaluating data sensitivity, regulatory requirements, and operational needs before organizational adoption. For sensitive business communications, consider purpose-built enterprise platforms with administrative controls, compliance certifications, and audit capabilities consumer messaging platforms lack. If consumer platforms selected, implement supplementary organizational controls (policies, training, monitoring, archiving) compensating for platform limitations.
Share
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Angry
0
 Sad
0
 Wow
0